
Post-quantum mobile credentials, on the PACS you already run.
Sentry post-quantum mobile credential technology works with your existing access control systems using our software-based translation layer. Designed to resist attacks from future quantum computers, the technology provides advanced protection for mobile credential identity and authentication.
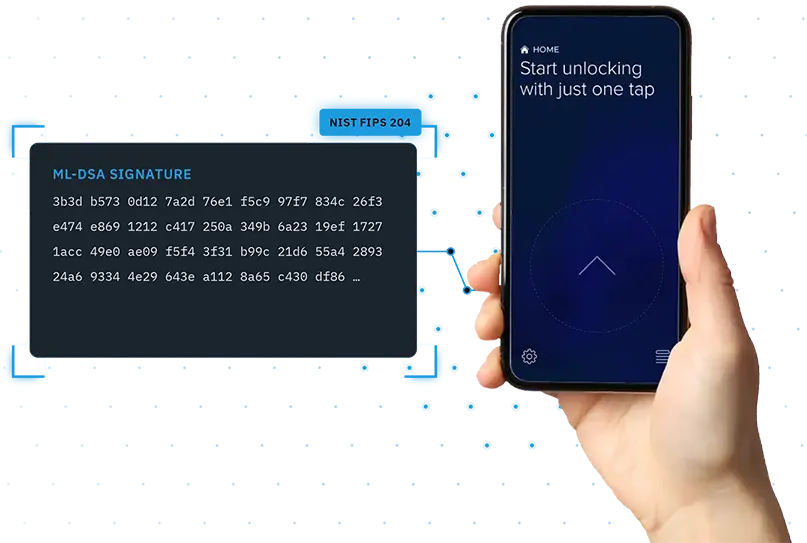

No reader replacement
Post-quantum mobile credentials use the mobile phone as the virtual reader paired with a Sentry Smart Access Tile, removing reader hardware dependencies
No PACS replacement
Your access control system stays exactly as it is. A software-based translation layer is installed on to your computer that allows your PACS to receive Sentry’s post-quantum credentials.
NIST FIPS 204
Mobile credentials are signed with ML-DSA, the NIST post-quantum signature standard.
Plan for quantum before it arrives, not after.
Designed to resist attacks from future quantum computers, Sentry’s post-quantum credential technology provides advanced protection for mobile credential identity and authentication. Delivering stronger security today while giving customers the flexibility and freedom to modernize their existing access control systems on their own terms.
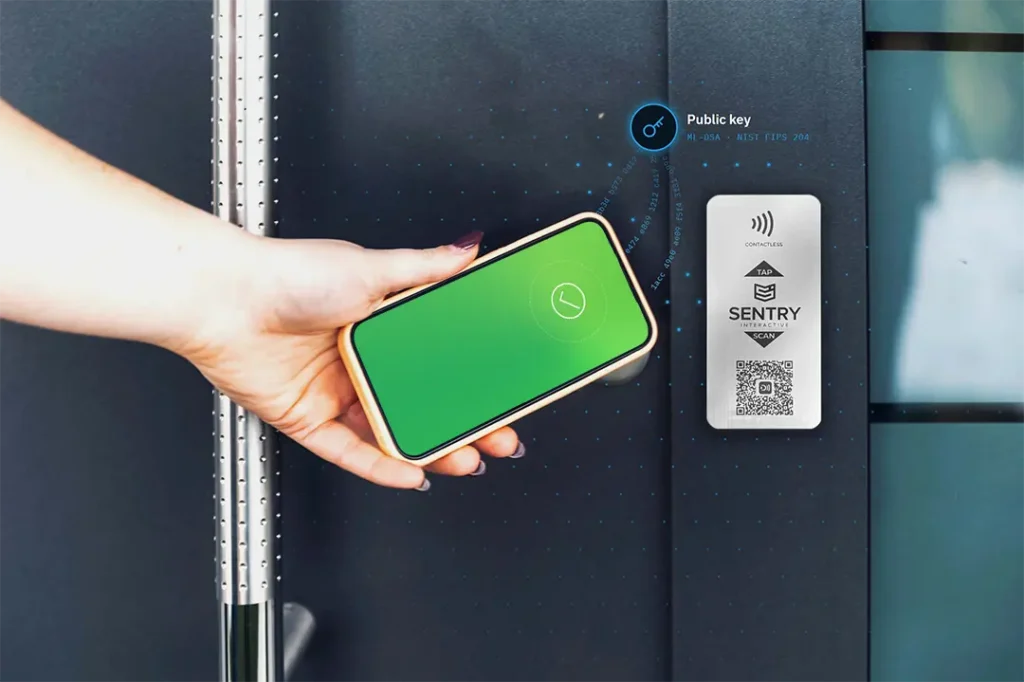
Integration with your existing PACS infrastructure
Moving to post-quantum security usually sounds like a rip-and-replace project. It isn’t. Sentry secures the credential layer; your PACS keeps the decision layer. The translation layer is what connects the two.
| What Sentry adds: the post-quantum credential layer | What stays the same: your PACS and everything behind it |
|---|---|
Post-quantum NFC mobile credentials enrolled through Sentry Open Credential over IP |
Your PACS makes the final access decision |
Public keys signed with ML-DSA and verified by the Sentry Cloud |
Every unlock event is logged exactly as it is today |
Private keys that never leave the user’s mobile device |
Existing panels stay in place |
Credentials that remain post-quantum protected across Sentry’s network |
Existing reader hardware stays in place |
Wireless passive NFC Sentry Smart Access Tiles at each door |
|
Software-based post-quantum translation layer for your existing PACS computer |
A post-quantum solution for the access control system you already trust
The post-quantum translation layer
Sentry’s post-quantum translation layer is a standalone application that runs on a computer between the Sentry Cloud and your PACS. It converts each post-quantum credential into a credential format your PACS recognizes so the PACS continues to make the final access decision and log each event exactly as it does today.
The result: sites can isolate legacy, weaker signaling behind a post-quantum, cryptographically verified front end without ripping out panels or wiring.
In
Post-quantum unlock request
From the Sentry Cloud, signed and verified with ML-DSA
On your server
Translation layer
Converts to a credential format your PACS understands
Out
Conventional PACS credential
Your PACS decides and logs, exactly as before
How do post-quantum mobile credentials work?

Enroll
Sentry creates a post-quantum credential and delivers it to the user’s phone. The user signs up to it. The private key is stored on the phone.

Tap
The user taps a Sentry Smart Access Tile. A post-quantum unlock request travels across Sentry’s post-quantum protected network.

Translation
The translation layer converts the request into a conventional credential that your existing PACS can understand.

Decision
Your PACS continues to make the final unlock decision and logs the event.
Built on readerless architecture
Sentry post-quantum mobile credentials work with Sentry Smart Access Tiles.
Sentry Smart Access Tiles can be mounted next to doors without wiring. When interacted with they identify the access point the user wishes to enter using their post-quantum mobile credentials.

What's the difference between conventional and post-quantum cryptography for mobile credentials?
Conventional
RSA and elliptic-curve cryptography
Widely used today, and expected to be vulnerable to quantum attacks.
Post-quantum – NIST FIPS 204
ML-DSA
The Module-Lattice-Based Digital Signature Algorithm, designed to resist attacks from future quantum computers. Sentry uses it to protect mobile credential identity and authentication.
Start enrolling post-quantum credentials on your existing PACS
Talk to our team today about how you can protect your access control from quantum computing by implementing Sentry’s post quantum mobile credentials and translation layer.
Frequently asked questions
No. Your existing access control system and readers stay in place. Sentry adds a software-based translation layer, installed on a computer alongside your PACS, plus wireless passive NFC Sentry Smart Access Tiles at each door. The user’s mobile phone is the virtual reader and your PACS still makes every access decision and logs every event exactly as it does today.
ML-DSA (Module-Lattice-Based Digital Signature Algorithm) is the post-quantum digital signature standard published by NIST as FIPS 204. It is designed to resist attacks from both conventional and quantum computers. Sentry post-quantum mobile credentials are signed with ML-DSA and verified by the Sentry Cloud, so credential identity and authentication rely on a recognised standard.
The credential layer is post-quantum protected. This includes credential issuance through Sentry Open Credential over IP, ML-DSA signing and verification, and the unlock request travelling across Sentry’s network. The translation layer then converts each verified credential into a format your PACS already recognises. This lets you isolate legacy, weaker signalling behind a post-quantum, cryptographically verified front end without changing what sits behind it.
Access control infrastructure is typically in place for 10 to 15 years or more, so the systems installed today will still be running when quantum computers become a practical threat. A capable quantum computer could break the signature algorithms most mobile credentials rely on today, which would allow an attacker to forge a valid credential. Sentry’s post-quantum mobile credential layer allows organizations to stay ahead of threats without changing their PACS hardware.
The translation layer is a standalone application installed on a computer that sits between the Sentry Cloud and your PACS. When a user taps a Sentry Smart Access Tile, the Sentry Cloud verifies their post-quantum credential. The translation layer then converts it into a credential format your PACS already recognises. Your PACS receives the credential as it would from any existing reader, makes the access decision, and logs the event as normal. There is no new hardware to install, it is completely software based.